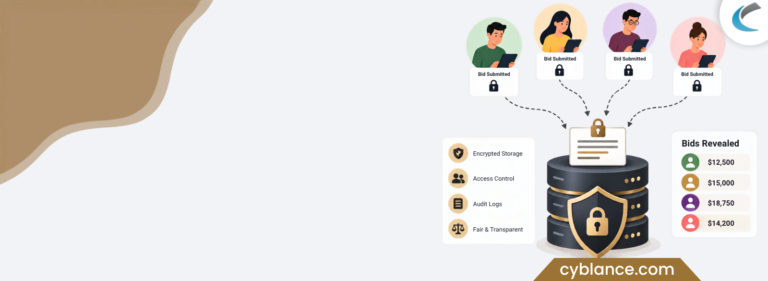


Imagine a bidder winning a $2 million piece of artwork using a stolen identity or funds linked to a sanctioned entity. Without proper KYC and AML controls, the platform, not just the bidder- could face regulatory scrutiny, financial penalties, and reputational damage. That’s why KYC and AML compliance is no longer an optional feature for online auction platforms.
This post is a technical walkthrough for developers and product teams: what identity verification actually needs to look like, how biometric checks fit into the bidding funnel, how screening against watchlists works under the hood, how deposit enforcement ties into bid eligibility, and how to structure audit trails that will actually survive a regulator’s scrutiny.
Why Auction Platforms Are a Distinct AML Risk Category
Most KYC/AML guidance online is written for banks, fintech apps, or crypto exchanges. Auction platforms have a different risk shape:
- Irregular, high-value transactions. Unlike a subscription app with predictable monthly charges, an auction platform might see a single user place one bid worth $500,000 and never transact again. This breaks conventional transaction-monitoring models built around recurring patterns.
- Bidder anonymity by design. Traditional auction houses built their brand on discretion. Digital platforms inherit that expectation, which conflicts directly with the need for verified identity.
- Cross-border participants. A single auction lot can attract bidders from a dozen jurisdictions simultaneously, each with different KYC thresholds, sanctions regimes, and reporting obligations.
- Asset laundering risk. High-value collectibles, art, and real estate are classic vehicles for placing or layering illicit funds, since valuation is subjective and resale is straightforward.
This is why AML compliance bidding platform design has to be treated as a first-class architectural concern, not a form embedded somewhere in account settings.
Two-Tier KYC Models: Light vs. Full Verification
Not every user needs the same depth of verification, and forcing full KYC on every visitor kills conversion. The standard approach developers should design for is a tiered verification model, gating access progressively as financial exposure increases.
Tier 1 – Light KYC (Browsing and Low-Value Bidding)
This tier typically covers:
- Email and phone verification
- Basic personal details (name, address, date of birth)
- A soft identity check against public data sources
- A bid ceiling, often capped at a low fixed value or a percentage of the lot’s estimated worth
Light KYC lets a platform onboard casual browsers and low-stakes bidders quickly, preserving the frictionless experience users expect from e-commerce-style interfaces.
Tier 2 – Full KYC (High-Value and Regulated Lots)
Once a bidder crosses a defined threshold, a specific lot value, a cumulative bidding total, or participation in a regulated asset category like real estate or vehicles, the system should force an upgrade to full verification, which includes:
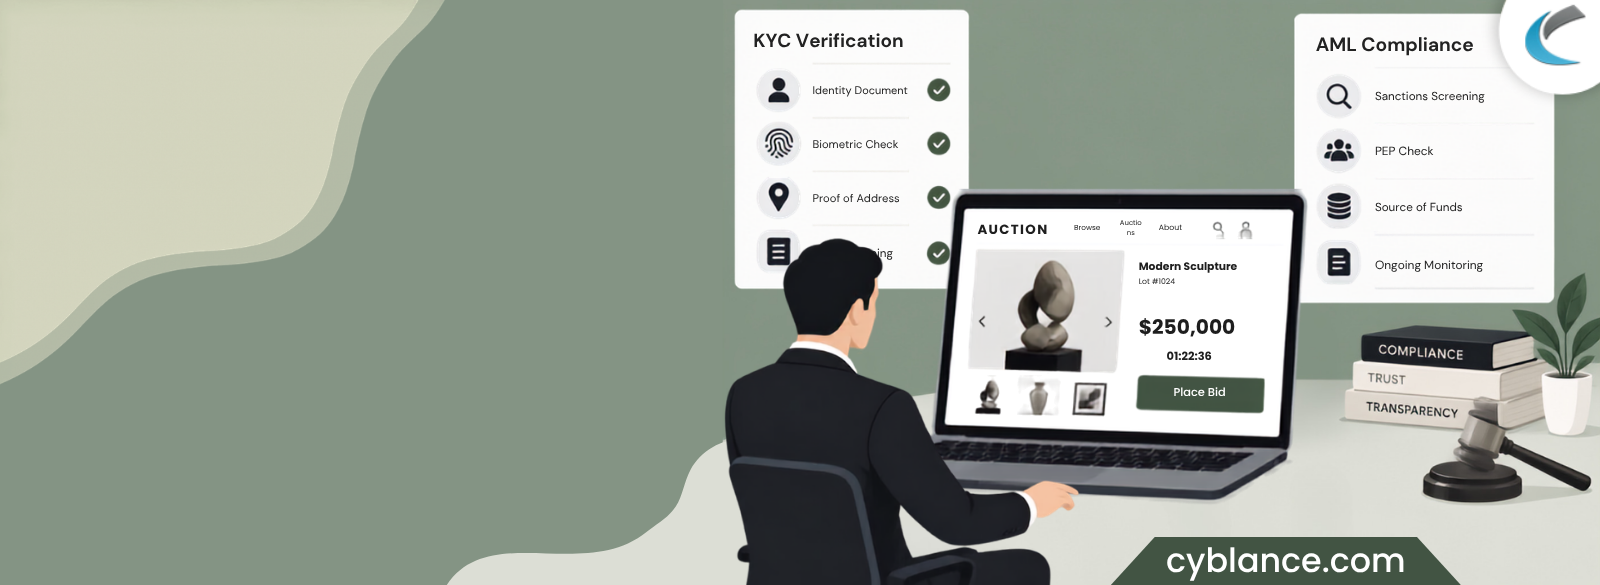
- Government-issued ID document capture and validation
- Biometric liveness and face-match verification
- Proof of address
- Source-of-funds declaration for high-value lots
- PEP and sanctions screening
- Enhanced due diligence (EDD) for flagged profiles
From an engineering standpoint, this means the bidding engine must check the verification tier before allowing a bid to register, not after settlement. The gate belongs in the bid-submission service, with tier status stored as a first-class attribute on the user object and re-validated server-side on every bid request, never trusted from client state.
bid_request → check(user.kyc_tier) →
if lot_value > tier.threshold → block + trigger_upgrade_flow
else → proceed_to_bid_engine
Identity Document Verification: The Technical Building Blocks
Identity verification for online auctions typically runs through a pipeline of discrete steps, usually delegated to a specialized verification provider via API rather than built entirely in-house:
- Document capture – OCR extraction of ID fields (name, DOB, document number, expiry) from a photo or scan.
- Document authenticity checks – Detection of tampering, font inconsistencies, hologram or MRZ (machine-readable zone) validation, and cross-checks against known document templates by issuing country.
- Data cross-validation – Matching extracted data against user-submitted profile data and, where available, government or credit bureau databases.
- Risk scoring – A composite score combining document confidence, geographic risk, and behavioral signals (device fingerprint, IP geolocation mismatch, VPN detection).
Developers should design this as an asynchronous, event-driven process. Verification providers rarely return results instantly for full checks, so the bidding UI needs a clear “pending verification” state, with webhooks updating the user’s KYC status once the provider completes its checks. Don’t block the entire application on a synchronous call to a third-party verification API, that’s a reliability and latency risk that will surface exactly when traffic spikes during a popular auction.
Biometric KYC and Liveness Matching
Biometric KYC auction software adds a second identity layer on top of document verification: proving that the person submitting the document is physically present and matches the photo on the ID.
The typical flow:
- The user captures a live selfie or short video through the platform’s camera SDK.
- A liveness detection model checks for signs of a real, present human, blinking, head movement, depth cues, to defeat photo, video replay, or deepfake spoofing attempts.
- A face-match algorithm compares the selfie against the photo extracted from the ID document, returning a similarity confidence score.
- Results above a configured threshold auto-approve; results in a gray zone route to manual review; low scores trigger rejection or a request for resubmission.
For platforms operating internationally, it’s worth building liveness and face-match as a pluggable module rather than hardcoding a single vendor’s SDK. Regulatory acceptance of biometric verification varies by jurisdiction, and some regions require additional consent flows or data localization for biometric data storage, which affects where and how you’re allowed to persist face-match templates.
A practical note: biometric data is typically classified as sensitive personal data under privacy regulations. Store only the derived match score and a reference to the verification event, not the raw biometric template, unless your legal counsel has explicitly signed off on retention requirements for your target markets.
PEP and Sanctions List Screening
PEP screening auction platform requirements exist because politically exposed persons and their close associates carry elevated corruption and bribery risk, and sanctioned individuals or entities are legally barred from participating in financial transactions in most jurisdictions.
At the architecture level, screening should run:
- At onboarding, against global sanctions lists (OFAC, UN, EU consolidated lists, and relevant domestic lists), PEP databases, and adverse media sources.
- On an ongoing basis, since sanctions lists update frequently, a previously clean user can become flagged mid-relationship. This requires a scheduled rescreening job, not a one-time check at signup.
- Fuzzy-matched, using name-matching algorithms tolerant of transliteration differences, aliases, and common spelling variants, exact-string matching will miss the majority of genuine hits.
Screening is almost always delegated to a specialized compliance data provider via API, since maintaining accurate, current sanctions and PEP data in-house is a full-time regulatory undertaking on its own. The platform’s responsibility is to integrate that screening cleanly into the onboarding and periodic-review workflow, log every screening event with a timestamp and list version, and route true or potential matches into a case-management queue for compliance officer review rather than auto-rejecting on a fuzzy match alone.
EMD (Earnest Money Deposit) Enforcement Before Bid Eligibility
This is one of the more auction-specific pieces of the compliance stack. Deposit enforcement auction system logic ensures bidders have skin in the game and that funds tied to a bid are provably available, both a fraud-prevention measure and, in many jurisdictions, a regulatory requirement for high-value lots like real estate or vehicle auctions.
The mechanics developers typically need to implement:
- Pre-authorization or escrow hold – Before a user is allowed to place a bid on a deposit-gated lot, the platform authorizes or escrows a percentage of the estimated lot value (commonly 5–10%) via a payment processor or escrow partner.
- Bid eligibility gate – The bid-submission service checks for an active, sufficient deposit hold tied to that specific lot (or auction event) before accepting the bid. This should be a hard server-side check, never enforced only in the frontend.
- Deposit release or capture logic – For losing bidders, the hold is released automatically once the auction closes. For the winning bidder, the deposit converts into a partial payment or is captured against the final settlement amount.
- Reconciliation – A scheduled job reconciles deposit holds against payment processor records to catch orphaned holds, failed releases, or discrepancies before they become compliance or customer-service issues.
Building this as a dedicated deposit-ledger service, separate from but tightly coupled to the bidding engine, makes it far easier to audit and reduces the risk of a race condition where a bid is accepted without a valid deposit due to timing issues between services.
Audit Trail and Regulatory Reporting Requirements
Every compliance control described above is only as good as its evidentiary trail. Regulators and auditors will ask not just “did you screen this user” but “prove it, with a timestamp, the data source version, and who reviewed it.”
A robust audit architecture should log, at a minimum:
- Every KYC tier change, with the triggering event and timestamp
- Every document verification attempt, result, and confidence score
- Every biometric verification event, result, and reviewer (if manually escalated)
- Every screening run against sanctions/PEP lists, including the list version.
- Every deposit is held, captured, and released, tied to the specific lot and user
- Every manual compliance decision is made with the reviewing officer’s identity.
These logs should be immutable, append-only storage, ideally with cryptographic hashing or a write-once storage layer, so records can’t be altered after the fact. Structuring this as a dedicated compliance-events service, separate from general application logs, makes it far easier to generate regulator-ready reports (such as Suspicious Activity Reports or jurisdiction-specific equivalents) on demand rather than reconstructing history from scattered application logs under time pressure.
Bringing It Together: A Reference Architecture
At a high level, a compliant auction platform’s identity and risk layer typically looks like this:
- Identity Verification Service – Orchestrates document and biometric checks via third-party providers, exposing a unified KYC status API to the rest of the platform.
- Screening Service – Handles sanctions/PEP checks at onboarding and on a recurring schedule, feeds a compliance case-management queue.
- Deposit Ledger Service – Manages EMD holds, captures, and releases, tightly integrated with the bidding engine’s eligibility checks.
- Compliance Event Log – Immutable, centralized audit trail consumed by reporting and regulator-facing tooling.
- Bidding Engine – The only service permitted to accept bids, and the enforcement point where KYC tier, screening status, and deposit state are all validated server-side before a bid is registered.
Decoupling these into distinct services, rather than embedding compliance logic directly inside the bidding engine, keeps the system auditable, testable, and adaptable as regulatory requirements shift across the markets a platform operates in.
Final Thoughts
Compliance in auction platforms isn’t a feature you ship once, it’s an operating discipline that has to evolve alongside changing regulations, new fraud patterns, and expansion into new jurisdictions. Getting the foundational architecture right in 2026, tiered KYC, biometric verification, continuous sanctions screening, enforced deposits, and an unimpeachable audit trail, makes every future regulatory change a configuration update rather than a rebuild.
Building KYC and AML into your platform from day one is far more cost-effective than retrofitting compliance later. If you’re planning or scaling an online auction platform, working with an experienced development team can help you design a compliant, scalable architecture that meets both operational and regulatory requirements.
FAQs
EMD (Earnest Money Deposit) is a refundable security deposit that bidders must provide before participating in certain auctions. It helps verify bidder intent, discourages fraudulent bidding, and can be adjusted against the final purchase price for the winning bidder.
In many cases, yes. While requirements vary by jurisdiction and asset type, auction platforms handling high-value transactions, regulated assets, or cross-border bidders often implement Know Your Customer (KYC) verification to comply with anti-money laundering (AML) regulations and reduce fraud risk.
Anti-Money Laundering (AML) refers to the policies, processes, and technologies used to detect and prevent financial crimes. In an auction platform, AML measures may include identity verification, sanctions and PEP screening, transaction monitoring, and maintaining audit trails for regulatory compliance.
Sanctions and Politically Exposed Person (PEP) screening help identify individuals or entities that may pose legal, financial, or reputational risks. Regular screening enables auction platforms to comply with regulatory requirements, reduce exposure to financial crime, and prevent prohibited transactions.